Describe the system in prose. Netras extracts the components, the data flows and the trust boundaries, then works STRIDE, PASTA, DREAD and NIST CSF over that model. Every claim in the report is either established by your description or marked as an open question.
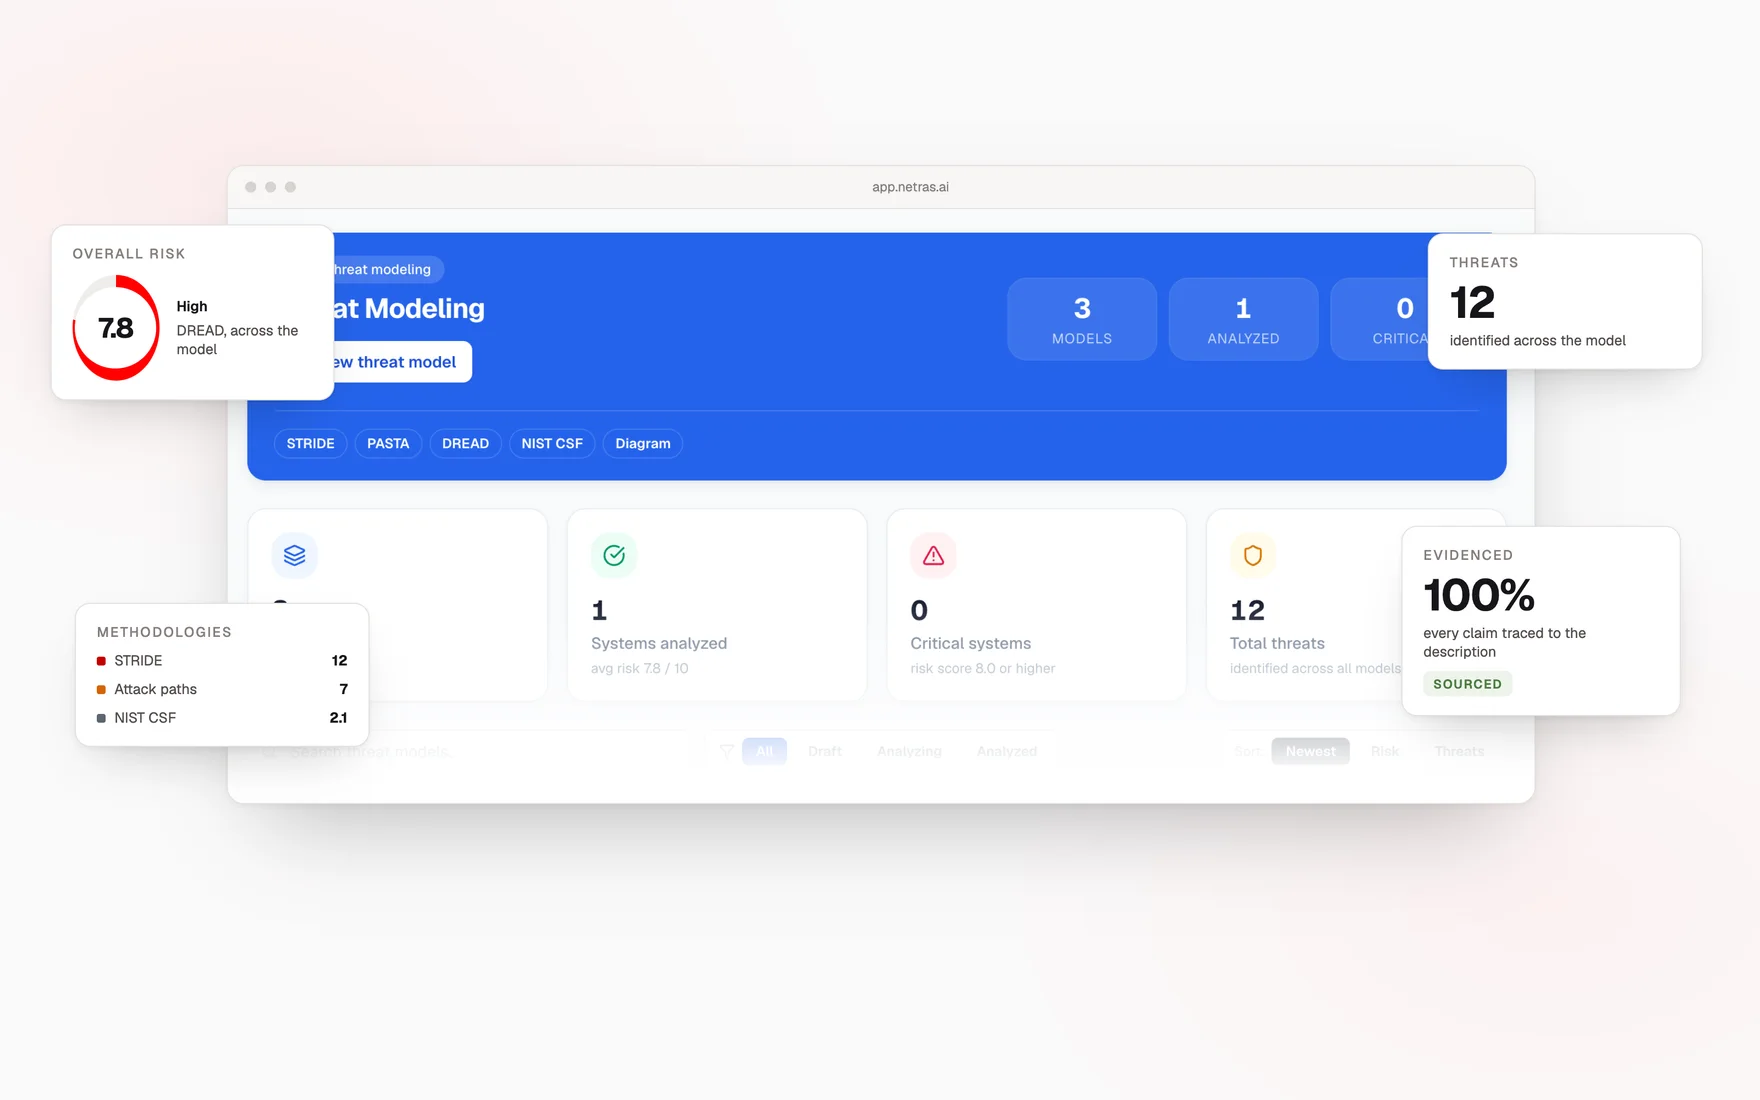
The model is built once from your description. Each methodology then asks its own questions of that same model, which is why the answers do not contradict one another.
Components, data flows, trust boundaries and entry points, pulled from prose and shown back to you as a diagram you can correct before anything is scored.
Spoofing, tampering, repudiation, information disclosure, denial of service and elevation, raised against the elements they can actually apply to.
From business objectives through to attack modelling and risk analysis, with the weaknesses it asserts downgraded where your description does not support them.
Damage, reproducibility, exploitability, affected users and discoverability, scored so the ranking separates threats rather than putting everything at nine.
A route is a chain through real data flows. A path cannot invent a door that your architecture does not have, which is the usual failure of generated threat models.
Identify, protect, detect, respond and recover, scored against the description with the gaps under each function stated as the questions that would settle them.
The deliverable is a report, not a screen. It carries the diagram, the threats, the attack paths, the blast radius, the business-logic coverage, the security debt, the compliance exposure and a sequence to do the work in, each numbered and cross-referenced.
No. You write a description of the system and the platform produces the diagram. You can correct it, and the correction feeds the model rather than sitting beside it.
The extraction and the first pass are. Everything published is then checked against your description: a claim the description does not support is weakened or turned into an open question, never strengthened.
Yes, and the previous version is kept. A regenerated model does not quietly discard the recommendations somebody had already accepted.
A working demo with your data shape, not a slide deck.