A cybersecurity venture built to help organisations find security gaps before attackers do. Offensive security, compliance advisory and remediation guidance, delivered as one connected engagement.
Built to help organisations find security gaps before attackers do.
Certified experts lead every engagement, accelerated by advanced models.
Developer-ready remediation guidance for every finding, not just a report.
Audit-ready reporting aligned to the frameworks your regulators expect.
We combine hands-on offensive testing with AI-accelerated coverage and custom, developer-ready remediation guidance for every finding.
Request an assessmentCertified security experts lead every engagement from day one, not just automated scanners. Advanced models surface loopholes manual testing alone can miss.
Actionable fixes your team can implement fast, with step-by-step remediation guidance. One contract, one team, for testing, guidance and compliance.
Testing aligned to OWASP, PTES and NIST SP 800-115, continuously refreshed to track emerging attack techniques.
GRC advisory aligned to UAE, KSA and global frameworks. ISO 27001, SOC 2 and NIST-aligned audit-ready reporting.
Pentesting as a service: tests the running app the way a real attacker would.
Source code review and composition analysis, before code reaches production.
iOS and Android testing: static, dynamic and runtime analysis.
REST and GraphQL testing, authentication and business-logic flaws.
Policies, risk registers and audit readiness, built around your business.
Fractional security leadership, without a full-time hire.
NESA, DESC, UAE PDPL, NCA ECC and SAMA readiness.
ISO 27001, SOC 2, NIST CSF and GDPR guidance.
A test tells you where you stood on the day. The platform is how the answer stays current: findings with an owner and a date, controls that re-check themselves, and evidence that records when it was last proven.
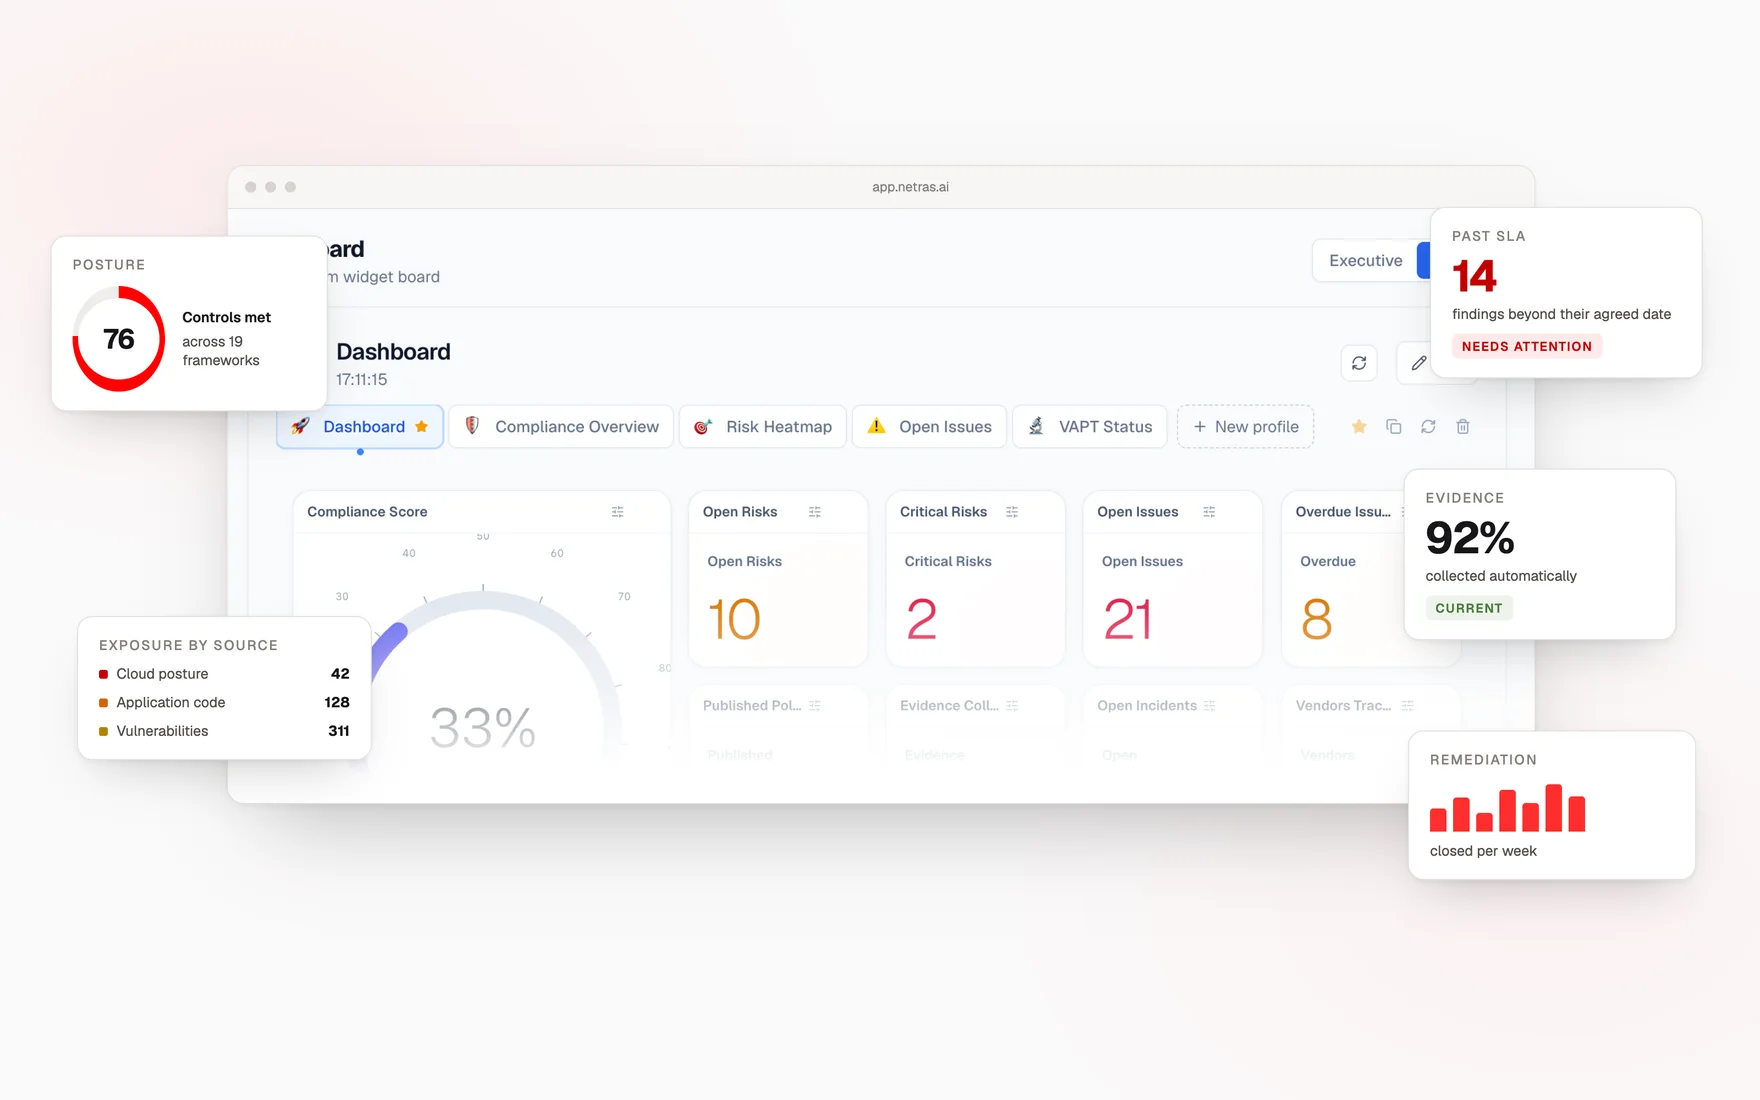
Continuous discovery across cloud, code, containers and the public internet, with per-asset posture derived from configuration.
Read moreFindings with an owner, a business unit and an SLA, from import through re-test to a fix somebody signed off.
Read moreSTRIDE, PASTA, DREAD and NIST CSF worked over the architecture you described, with attack paths from the graph.
Read moreVendor assessments, evidence collection and a portal vendors can use without buying anything.
Read moreNineteen frameworks on one control set, with automated checks and evidence that knows when it was last proven.
Read moreOne inventory joining cloud assets, devices, people and their accounts, so ownership is a fact rather than a guess.
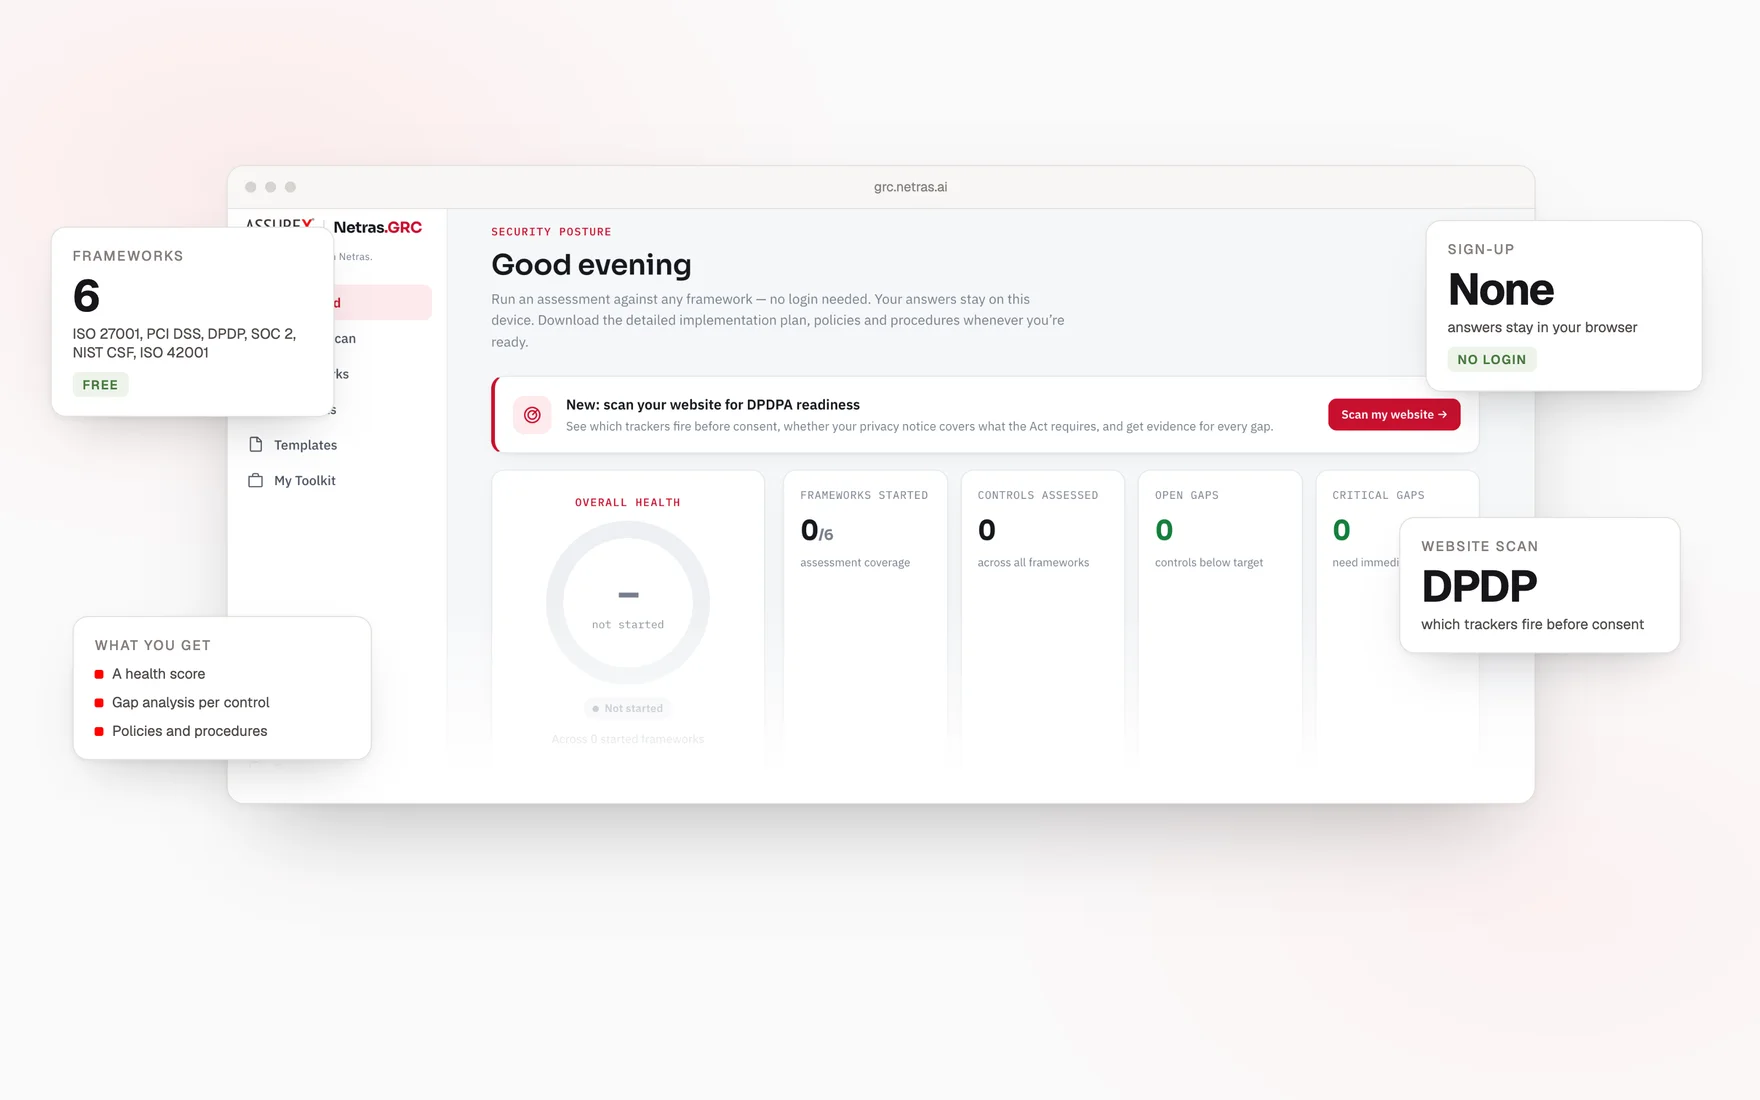
Read moreNetras.GRC is our free assessment. Pick a framework, answer against the real control set, and get a health score, a gap analysis and the policies to close them. No account, no sales call, and your answers stay in your browser.
PCI DSS and SWIFT CSP alignment, fraud and transaction security testing.
HIPAA and GDPR, medical device and clinical system assessment.
On-premises deployment, NIST CSF and 800-53, segregated auditor access.
SOC 2 and ISO 27001 from one control set, with a trust centre.
PCI DSS 4.0 scope, shadow asset detection, peak-season readiness.
IT and building-system discovery, segmentation and contractor access review.
Netras is headquartered in the United Kingdom, backed by the Assurex Group's global delivery network, with offices in the UAE and the USA.
More about NetrasTell us what you are building. A scoped plan comes back within 48 hours.